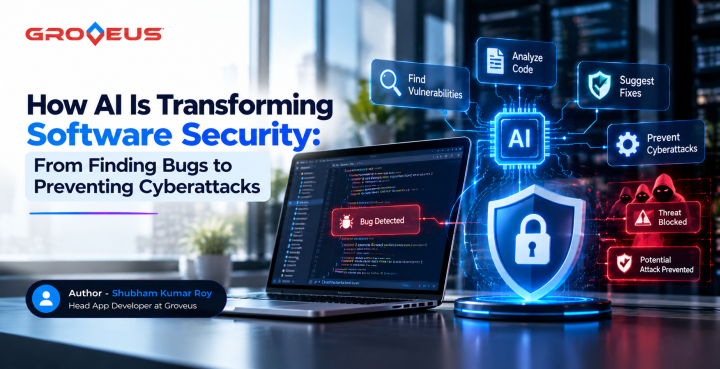
Discover how AI is transforming software security by detecting code vulnerabilities, helping prevent cyberattacks, improving security testing, and supporting developers in building safer applications.
Not long ago, a serious vulnerability usually turned up after a researcher spent weeks inside code they didn’t write. AI is shortening that process and this helps defenders and attackers too.
From Manual Review to AI-Assisted Security
Models can now read a large codebase, point out code that looks risky, guess how a bug might be triggered and write tests to check the guess. For a small team, code nobody had time to review can finally get a look.
The catch is that many of these tools' reports are wrong. The PHP Foundation says AI-assisted research has sharply increased the reports reaching PHP’s security team. Since 1 July, the team has closed approx more than 100 reports that were invalid, duplicates or couldn’t be reproduced. AI helps them sort through the pile, but a person still decides what’s real and writes the fix.
PHP2Shell: A Real-World Example
In October 2026, PHP patched two critical flaws in its core engine, CVE-2026-109618 and CVE-2026-109619. In certain setups, they let an attacker run code on a server without logging in.
The root problem wasn’t new. A PHP Foundation developer had noticed it in 2024, but no practical exploit was known. This year Calif, OpenAI and Wiz each reported working attack paths. Calif and Wiz used models from OpenAI and Google, and Wiz built proof-of-concept exploits against test systems. PHP’s own team wrote, tested and released the fix.
The potential impact was global. PHP powers 70% of the world’s websites whose server side technology is based on it. But this doesn’t mean that 70% of the world's websites were at risk. But it shows how a single flaw can put a huge number of systems at risk.
AI Helps Attackers Too
Wiz says AI made it practical to adapt its exploits to different PHP versions and server setups. That was research, not an attack. But criminals have access to similar models, so a bug that once looked too hard to exploit is riskier to leave unpatched than it used to be.
What This Means for Developers
If you use AI, treat it as a second reviewer rather than the only one. Keep automated security tests in your pipeline, and don’t act on an AI-reported issue until someone has reproduced it. Update PHP and other dependencies promptly, since AI may also help attackers study a published fix and build an exploit from it faster. Review AI-written code like a new hire’s first pull request.
The Real Lesson
AI is making bugs easier to find, and that cuts both ways. Whether your systems get safer still depends on the basics i.e. test your fixes, keep your software updated and make sure someone on the team understands how it all works.
Comments 0